Offshore Staff in a Tax Practice: Section 7216 Consent, WISP and Data Security
Yes. A U.S. tax firm can use staff outside the United States if two things are in place first. Clients must sign a Section 7216 consent that includes the mandatory language for preparers abroad, and the firm must keep a Written Information Security Plan and meet the FTC Safeguards Rule, with remote access covered in both.
Can a US tax firm use staff outside the US?
A U.S. tax firm can use staff outside the U.S. for return work, provided the firm gets client consent under IRC Section 7216 with the language Rev. Proc. 2013-14 requires for preparers located abroad. The firm also needs a Written Information Security Plan and a Safeguards Rule program that cover the remote staff's devices, logins and access.
Plan on owning this setup inside the firm, however you find the person. The consent comes from your clients and the security plan describes your systems. Whoever signs the returns should also sign off on the consent forms and the security plan before the first client file is opened.
Most of the work is paperwork you do once and then maintain: a consent template, a section of the WISP, an access list and an offboarding checklist. Firms that settle it in the fall start January with a clean process. Firms that try to do it in February end up holding files back from the person they hired to help.
What does Section 7216 consent require for a preparer outside the US?
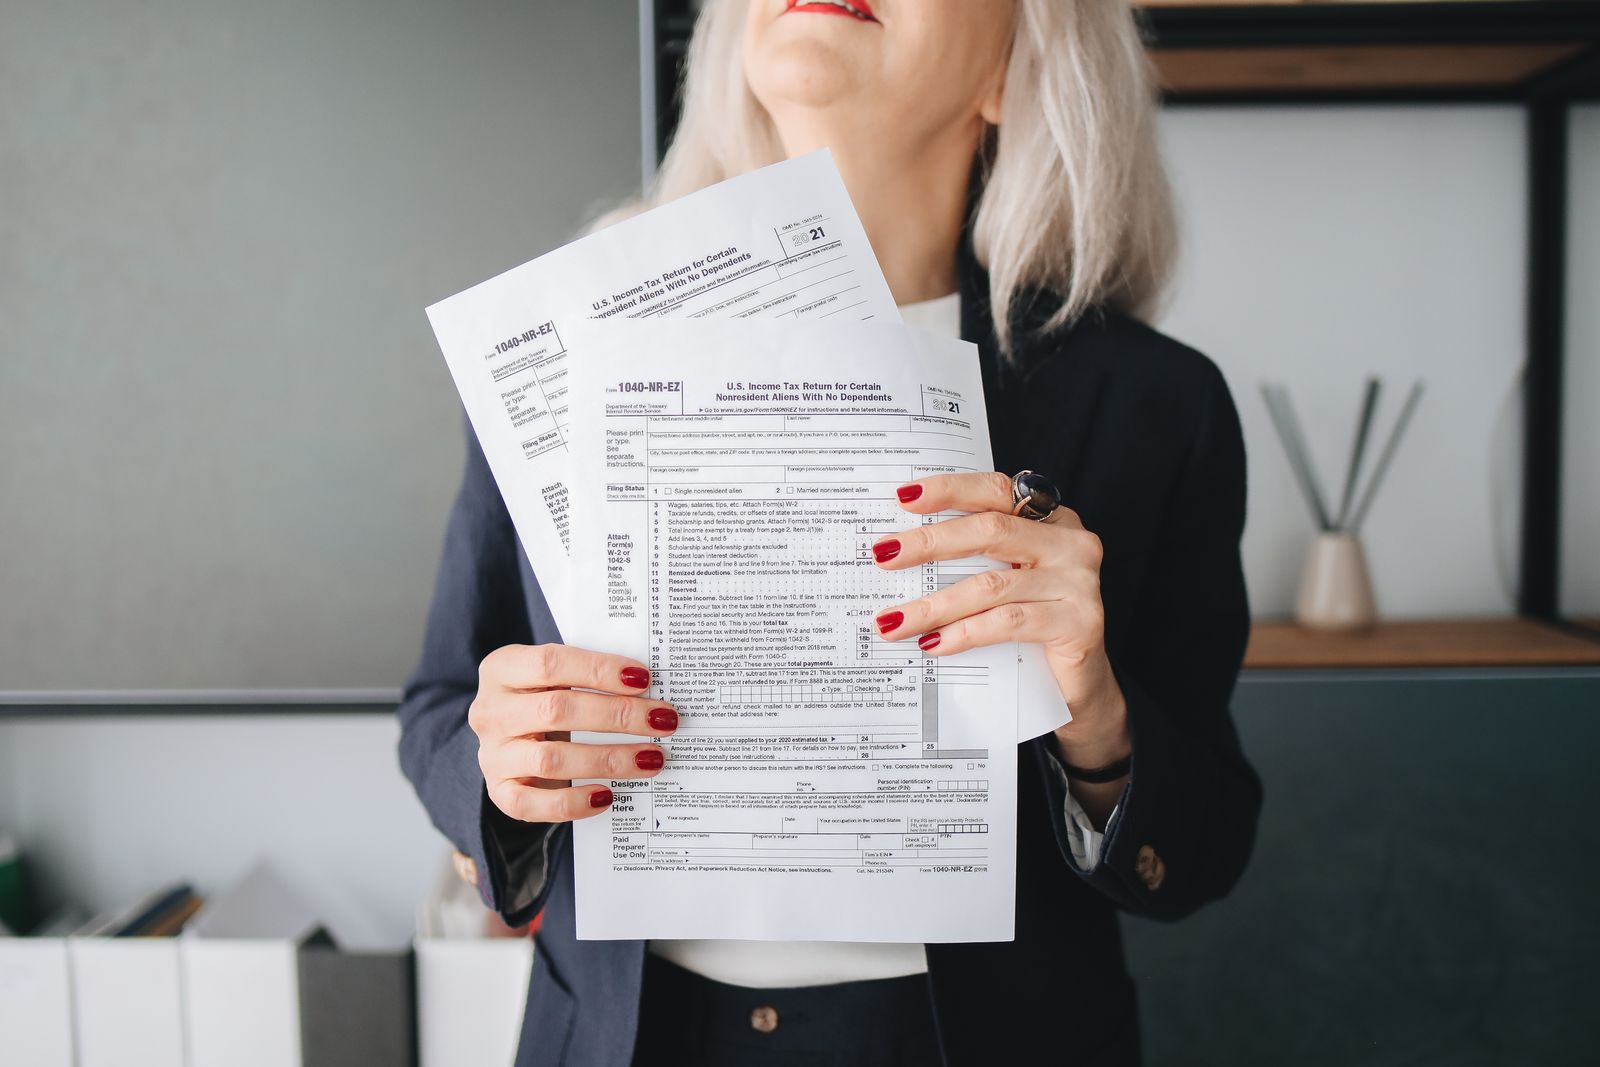
Section 7216 consent for a preparer outside the U.S. must carry mandatory language under Rev. Proc. 2013-14, warning the taxpayer that U.S. federal agencies "may not be able to enforce" U.S. privacy laws against the foreign preparer. If the client's SSN is disclosed, both preparers must keep an "adequate data protection safeguard" in place at consent and at disclosure.
Three practical points follow from the rule.
The consent comes before the disclosure. If a client's documents arrive in the portal in January and the signed consent comes back in March, the offshore assistant should not touch that file until March. Build the consent into the engagement packet so it goes out with the organizer and comes back with the signature.
The wording is fixed. The revenue procedure sets out the language, in sections 5.04(e)(ii) and 5.07. Paste it from the source into your template, then have your advisor confirm the template once. Avoid rewording it to sound friendlier.
The SSN rule pushes firms toward limiting what offshore staff see. If an assistant's job is document chasing and status calls, that assistant may not need full SSNs at all. Set up practice management and portal permissions so the assistant sees only what the task needs.
Clients who decline the consent are a normal outcome. Flag their files in practice management so only U.S. staff work them, and check the flag before any assignment.
What goes in the WISP when staff work remotely?
A WISP that covers remote staff states who has access to which systems, how devices are secured, how staff sign in, how files move, and what happens when someone leaves. The IRS template is Publication 5708, "Creating a Written Information Security Plan for Your Tax & Accounting Practice," and Publication 4557 lists recommended safeguards.
Federal law requires tax and accounting professionals to create and maintain the plan. For remote staff, the sections that most often need new text are these:
- Device rules: a dedicated work computer, full-disk encryption, screen lock, current operating system updates, and no client files on personal phones.
- Sign-in: multifactor authentication on email, the portal, practice management and tax software; a named account per person.
- File movement: client documents travel only through the portal or the firm's file system, never as email attachments or chat uploads.
- Access review: a monthly check that each person's permissions still match their tasks.
- Offboarding: same-day removal of every login, recovery of firm devices or a remote wipe, and a written record of both.
- Incident contact: the name of the person the remote staff member calls first if a laptop is lost or a phishing email gets clicked.
How does the FTC Safeguards Rule apply to a small tax firm?
The FTC Safeguards Rule applies to a small tax firm because tax preparation firms are listed as covered financial institutions. The Safeguards Rule requires a written information security program with administrative, technical and physical safeguards. Firms holding data on fewer than 5,000 consumers are exempt from certain provisions, so ask your advisor which parts apply at your size.
The breach notice rule is the part remote work makes more urgent. Since May 13, 2024, covered firms must notify the FTC "as soon as possible, and no later than 30 days after discovery" of a breach involving unencrypted information of at least 500 consumers. A firm with remote staff in another country needs a reporting path that works across that distance: the staff member reports to a named person the same day, and that person decides on notice.
Which controls should be in place before remote staff get access?
| Control | What it covers | Who owns it | When it must be done |
|---|---|---|---|
| 7216 consent template with offshore language | Client permission to disclose to a preparer abroad | Signing CPA or EA | Before engagement packets go out |
| Consent tracking flag in practice management | Which clients signed and which declined | Office manager | Before the first file assignment |
| WISP section for remote staff | Devices, sign-in, file movement, offboarding | Firm owner | Before access is granted |
| Named accounts with multifactor sign-in | Email, portal, tax software, practice management | IT lead or owner | First day of access |
| Field-level limits on SSNs | Who can see full identifiers | IT lead or owner | Before live client data |
| Confidentiality agreement | Duty to protect client data | Firm owner and staff member | Before training on real files |
| Incident and breach procedure | First call, decision on FTC notice | Firm owner | Before access is granted |
| Offboarding checklist | Same-day removal of logins and devices | Office manager | Written before day one |
Train on sample files until every row is done. A new assistant can learn the software, the naming rules and the review checklist on dummy returns without any consent issue.
Does the staff member's country change anything?
The staff member's country changes the working hours and, in one case, the payment checks. Bogota, Lima and Quito are on UTC-5 all year, the same as U.S. Eastern in winter and one hour behind during U.S. daylight time. Mexico City is UTC-6 all year, so it matches U.S. Central in winter (one hour behind Eastern) and falls two hours behind Eastern during U.S. daylight time.
For staff in Venezuela, U.S. sanctions are not a country-wide embargo, and OFAC states that the Venezuelan people are not subject to comprehensive sanctions. Executive Order 13884 blocks the Government of Venezuela and entities it owns, and OFAC keeps changing its general licenses. Screen every payee against OFAC lists and check current guidance before you pay.
For the work itself, which tasks a non-CPA assistant can take on sets the PTIN line, and the client intake and document collection workflow shows where consent tracking fits in the intake steps. Plan the security work into your tax season staffing calendar so it is finished in November. When the controls are ready, you can hire a financial assistant screened against your security plan.
How Remote Latinos can help
A remote hire is only as safe as the access you grant, so tell Remote Latinos on the first 30-minute call which client data the role will touch and which controls your WISP already has. Our recruiters vet candidates in Latin America against that scorecard, the person you pick works your hours inside your systems, and you make the final call after interviewing the shortlist. See the financial assistant role, then start a search for remote tax staff.
This article is general information, not legal or tax advice. Confirm the rules for your situation with a qualified advisor.
Frequently asked questions
What is the mandatory language in a 7216 consent for an offshore preparer?
Rev. Proc. 2013-14 requires a consent to disclose return information to a preparer outside the United States to include specific language. That language warns the taxpayer that U.S. federal agencies may not be able to enforce U.S. privacy laws against the foreign preparer. Use the exact wording from the revenue procedure rather than a paraphrase.
Does the 7216 consent cover the client's Social Security number?
It can, with an added condition. When the SSN is disclosed, both the U.S. preparer and the foreign preparer must maintain an adequate data protection safeguard when the consent is obtained and when the disclosure is made. A firm can also set up its workflow so offshore staff do not see full SSNs unless the task needs them.
Is a small tax firm exempt from the FTC Safeguards Rule?
No. Tax preparation firms are listed as covered financial institutions under the FTC Safeguards Rule. Institutions that hold data on fewer than 5,000 consumers are exempt from certain provisions only, so confirm with your advisor which ones apply to your firm.
What happens if remote staff are involved in a data breach?
The firm's obligations do not change because the staff member is remote. Since May 13, 2024, covered financial institutions must notify the FTC as soon as possible and no later than 30 days after discovering a breach involving unencrypted information of at least 500 consumers. The WISP should name who makes that call and how.
Sources
- Rev. Proc. 2013-14, Internal Revenue Bulletin 2013-3
- IRS news release IR-2026-92: Written Information Security Plan
- FTC: FTC Safeguards Rule, What Your Business Needs to Know
- FTC Business Blog: Safeguards Rule notification requirement
- OFAC FAQ 680
- OFAC FAQ 519
- OFAC Recent Actions, October 16, 2026
- IANA Time Zone Database: South America
- IANA Time Zone Database: North America